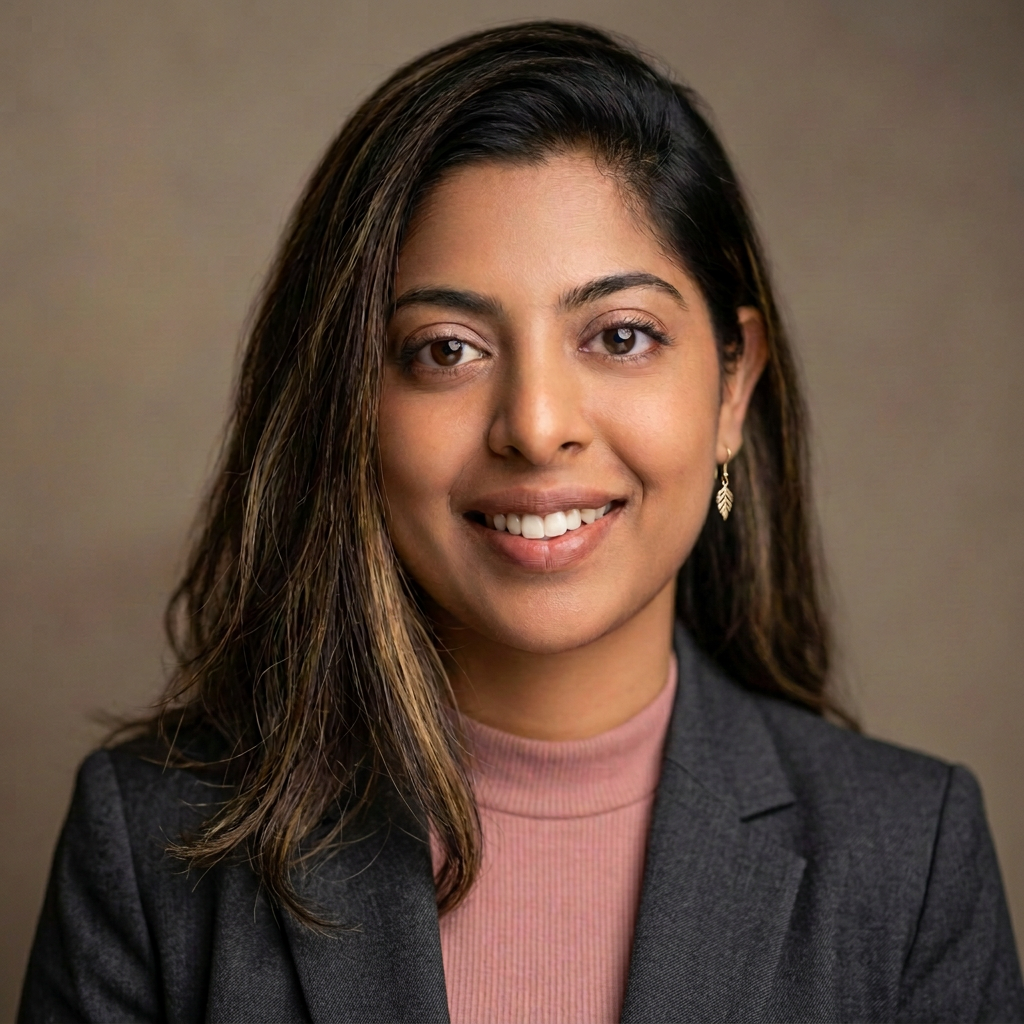
Priya ThapaSYSTEM ONLINE · NEW YORK

PriyaThapa

Senior Cyber Analyst · Threat Detection · Cyber Threat Intelligence

I investigate anomalous behavior, develop and tune detections, and turn security signals into actionable intelligence.

priya@research-ws: ~/portfolioILLUSTRATIVE

$ ./workspace --profile priya.thapa

  1. [INIT] Research workspace initialized
  2. [ANALYSIS] Behavioral anomaly investigation
  3. [DETECTION] Reviewing detection performance
  4. [INTEL] Emerging threat research
  5. [STATUS] Portfolio systems online

$

Visual storytelling only. Not real monitoring output.
40+tuning issues resolved
5+models independently developed
100+client deployments supported
50+intelligence briefings & reports
Source: 2026 resume · figures span different roles
01 · DEPLOYMENT HISTORY

Mission Logs

// tracking professional deployment history

  1. LOG_05

    Senior Cyber Analyst

    Darktrace

    Core member of the Model Development Team, resolving 40+ model-performance and tuning issues and independently developing 5+ detection models through experimentation and threat research.

    40+ tuning issues resolved5+ models developed
    Expand log
    • Lead high-priority, complex SOC investigations; analyze suspicious behavior and produce detailed SPOT reports that communicate findings, context, and analytical assessments.
    • Conduct threat research and hunting; contribute technical writing and team-wide presentations.
    • Mentor analysts through structured onboarding, weekly office hours, and hands-on labs; develop standardized workflows and training resources.
  2. LOG_04

    Cyber Analyst

    Darktrace

    Conducted real-time and retrospective SOC threat analysis, generating 5–7 daily Threat Intelligence Reports and detailed SPOT reports based on deep-dive investigations of suspicious behavior.

    5–7 daily intel reports10+ models co-developed
    Expand log
    • Analyzed datasets from hundreds to millions of records using Python, SQL, advanced Excel, and security analytics tooling; produced 2+ strategic threat trend reports over two years.
    • Collaborated with the model development team to create and optimize 10+ detection and response models. This is a collaborative contribution, distinct from independently developed models.
  3. LOG_03

    Cyber Technology Specialist

    Darktrace

    Principal technical liaison between clients, partners, and internal stakeholders; delivered 50+ tailored threat intelligence briefings and analytical reports and managed operational integrity across 100+ client deployments.

    50+ briefings & reports100+ deployments supported
    Expand log
    • Translated complex threat intelligence for audiences from SOC analysts to C-level executives.
    • Top-five ranking in the 2021 Darktrace RESPOND competition, Cyber Engineer and Technician (CET) category.
  4. LOG_02

    Cybersecurity Researcher and Content Writer

    Allari Inc

    Researched cybersecurity and cyberspace operations and authored more than 20 articles, translating complex security topics for the intended audience.

    20+ articles authored
  5. LOG_01

    Security and Compliance Analyst

    Consolidated Edison, Inc

    Worked with NERC CIP standards and Change Gear cybersecurity asset management. Assessed vulnerabilities on 20–30 lab assets, including HMIs, PLCs, and operational technology, using Metasploit, Nmap, and Nessus. Developed PowerShell and Bash automation for 100,000 files and folders.

    20–30 OT lab assets assessed
02 · SYSTEM INVENTORY

Capability Matrix

// verified tools and disciplines · no proficiency scores

MODULE_A

Threat detection & model development

Detection logic · tuning · model performance

  • Behavioral models
  • Detection-model tuning
  • Model performance analysis
  • Anomaly investigation

40+ tuning issues resolved · 5+ detection models independently developed Source: 2026 resume

MODULE_B

Threat investigation & hunting

SOC analysis · hunting · reporting

  • Threat investigations
  • Threat hunting
  • SPOT reporting
  • Threat intelligence reports
  • MITRE ATT&CK
MODULE_C

Security tools & analytics

Verified from resume

  • Darktrace
  • Wireshark
  • Snort
  • Splunk
  • Elastic Stack
  • OpenSearch
  • Nmap
  • Nessus
  • Shodan
  • Metasploit
  • Armitage
MODULE_D

Automation & foundations

Scripting · data · systems · frameworks

  • Python
  • SQL
  • Java
  • R
  • HTML
  • CSS
  • PowerShell
  • Bash
  • SQL Server
  • Firebase
  • IntelliJ IDEA
  • Spring Tool Suite
  • Spring
  • RESTful Services
  • MVC
  • GitHub
  • GitLab
  • SVN
  • Kali Linux
  • Ubuntu
  • Windows Server
  • NIST CSF
  • NERC CIP
Full searchable inventory
03 · CASE FILES

Classified Operations

// sanitized summaries · no proprietary logic or customer data

OP-01SANITIZED · PUBLIC SUMMARY

Detection model development & tuning

Challenge
Detection models generating performance and tuning issues that needed evidence-led evaluation.
My role
Core member of the Model Development Team: resolved 40+ model-performance and tuning issues; independently developed 5+ detection models.
Outcome
Documented resolution and model counts from my 2026 resume. Internal logic is not disclosed.
DarktracePythonSQLBehavioral analytics
Open case file
OP-02SANITIZED · PUBLIC SUMMARY

Behavioral threat investigation workflow

Challenge
Separating legitimate activity from behavior that warrants escalation.
My role
Lead complex SOC investigations and write SPOT reports. This case file is illustrative methodology, not a real incident.
Outcome
A repeatable signal → context → corroboration → assessment approach.
DarktraceWiresharkMITRE ATT&CK
Open case file
OP-03SANITIZED · PUBLIC SUMMARY

Threat intelligence to action

Challenge
Making emerging threats relevant to defenders and executives.
My role
Delivered 50+ briefings and reports; 5–7 daily threat intelligence reports as Cyber Analyst.
Outcome
Contributed to Darktrace’s public research and the 2026 Annual Threat Report.
Threat researchSplunkElastic Stack
Open case file
OP-04CON EDISON · 2019 to 2020

OT / ICS vulnerability assessment

Assessed vulnerabilities on 20–30 lab assets, including HMIs, PLCs and operational technology, under NERC CIP. Automated work across 100,000 files and folders with PowerShell and Bash.

MetasploitNmapNessusNERC CIP
04 · BRIEFING ARCHIVE

Threat Intelligence

// public research and contributions with source links

  1. BR-2026Threat landscapeAnnual Threat Report 2026Contributor · AMS-region material
  2. BR-2024-11SaaS · VPN exploitationBehind the Veil: Darktrace’s Detection of VPN Exploitation in SaaS EnvironmentsAuthor
  3. BR-2024-03Malware analysisSimulated vs. Real Malware: What You Need To KnowAuthor
  4. REFRansomware · behavioral detectionHiding in Plain Sight: Uncovering a Multi-Stage Ransomware Attack Through Behavioral DetectionBy Alexandra Evzona
05 · CREDENTIAL REGISTRY

Digital Vault

// education, certifications and recognition from resume & LinkedIn

// education

Master’s in Information TechnologyUniversity of the CumberlandsGPA: 4.0
Bachelor of Science in Computer Science Information System and SecurityJohn Jay College of Criminal Justice, CUNYGPA: 3.75 · Magna Cum Laude · Dean’s List Honoree
Associate’s degree in Computer ScienceLaGuardia Community College2016 to 2018 · LinkedIn profile

// certifications

Cisco Networking and Cybersecurity EssentialsNetworking and cybersecurity foundationsSource: 2026 resume
Darktrace AnalystDarktrace security analysisSource: 2026 resume
IBM Cloud for the EnterpriseEnterprise cloud foundationsSource: 2026 resume
Introduction to CybersecurityCybersecurity foundationsSource: LinkedIn profile PDF

// recognition

  • 2021Top five · Darktrace RESPOND competition, CET category
  • 20203rd place · ISACA Student Cybersecurity Case Competition, NY Metro
  • JJCExecutive Board Member · ISACA at John Jay College
06 · COMMUNITY

Leadership & Impact

// breaking into tech · women in cybersecurity · mentoring · education

MENTOR

CyberGirls Fellowship

Mentoring women entering cybersecurity through the CyberSafe Foundation, helping them find a path into tech, build confidence, and see themselves in the field.

VOLUNTEER

Microsoft TEALS

Volunteering in classrooms to introduce students to computer science and open a practical route into technology.

VOLUNTEER

Cyber Security Forum Initiative

Contributing to community initiatives that widen access to cybersecurity for people entering the field without an existing network.

MENTOR

Analyst development at Darktrace

Mentoring new analysts through structured onboarding, weekly office hours, and hands-on labs that help them find their footing and keep growing.

07 · SECURE CHANNEL

Open a conversation.

Threat detection, threat hunting, threat intelligence, and security research are the focus of my daily work. If you'd like to discuss any of them, reach me directly.